Reviewing us as a vendor? Start here.
last reviewed ·
We are a small firm asking to be trusted with access to systems that matter. This is what we would want to see if the roles were reversed — including the parts that are not finished yet.
Legal entity, jurisdiction and address
last reviewed ·
entity · Automated Solutions LLC · California · file no. 202359292696 · · California Secretary of State
AS DataWorks is the trading name for the data and Azure practice of Automated Solutions LLC, a California limited liability company (Secretary of State file no. 202359292696) based in San Diego, California. The registered address is deliberately not published. The AS DataWorks fictitious-business-name filing is in preparation; until it is filed we do not assert a registered DBA relationship. The full entity picture is on about.
At least five other active US businesses trade under "Automated Solutions" or a close variant, including one operating under the identical legal name "Automated Solutions, LLC." We are not affiliated with any of them, and nothing on this site describes their work. If a search result, directory listing or referral sent you here expecting a different company, check that you are reading asdataworks.com.
· Internal entity-name collision review
How we access client tenants
last reviewed ·
during an assessment · read-only · we change nothing
We hold ourselves to the same access standard we build for clients:
- Named individual accounts
- For every engineer who touches your environment. No shared credentials, ever.
- Least privilege by default
- Elevation is requested, approved by a named individual, granted for a fixed and logged time window, and returned automatically to no standing access — not standing administrator rights held indefinitely.
- Multi-factor authentication enforced
- On our accounts, including for administrators.
- Read-only access during assessments
- We inspect; we do not change configuration until you approve a plan.
- A documented offboarding process
- Executed at the end of an engagement and evidenced to you, not assumed.
- Subprocessors named before you sign
- Where any of your data is handled, listed in writing.
This is engineering discipline, not attestation — it makes an audit answerable, it does not replace the auditor.
Data handling and subprocessors
last reviewed ·
retention · not yet policy [PLACEHOLDER] period and data-subject contact
Website enquiries (the contact form) are stored in a Microsoft 365 SharePoint list inside our own tenant, and we are notified by Microsoft Teams and email. They are not sold, shared, or used for anything beyond replying to the enquiry.
| Subprocessor | What it does here | Data involved | Consent required |
|---|---|---|---|
| Microsoft | Hosting (Azure Static Web Apps) and Microsoft 365 (SharePoint, Teams, Power Automate) for form handling | Contact-form submissions; site hosting logs | No — required to operate the site |
| GitHub | Source control and CI/CD deployment of this website | Source code and build logs only — no visitor or form data | No |
| Plausible | Cookieless website analytics (page views, referrers) | Aggregate usage data — no cookies, no personal data | No — Plausible is cookieless by design |
| Google Ads | Advertising conversion measurement — not active at launch; added only if and when paid campaigns begin | Ad-click and conversion data, if and when enabled | Yes — consent-gated, denied by default under Consent Mode v2 |
Retention for non-converted enquiries is not yet adopted policy — 24 months is our own build documentation's recommendation, not a commitment — and there is no named data-subject request contact published yet. The privacy notice carries the version of both that ships today.
Our own security posture
last reviewed ·
next snapshot due · · the case study
Before recommending a tenant review to anyone else, we ran one on ourselves: the identity, licensing, sharing, device and email-authentication review we sell as the first step of an Azure migration.
secure score
52.1 / 64
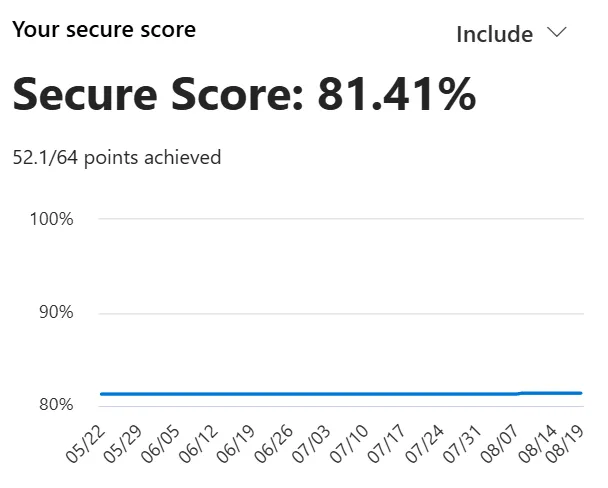
secure score panel · 81.41% — 52.1 / 64 · · Microsoft Secure Score, security.microsoft.com, our own tenant
Remediation of the findings is underway now. We are publishing the baseline today because it is real and checkable. We are deliberately not publishing the open finding list while it is still open — a public list of unremediated gaps in a live tenant is an attack map, not a trust signal. The baseline, the method and the outstanding after-number are written up at Microsoft 365 tenant hardening, which is where the second number and the list of what we chose not to fix will appear once remediation is complete.
Incident response
last reviewed ·
notification SLA · none published [PLACEHOLDER] a tested timeline
If we discover an incident affecting data we hold on your behalf — including a compromise of the systems behind the contact form — we will tell you directly, in plain language, as soon as we have facts we are confident are accurate. We do not have a published notification-timeline SLA yet, and we are not going to state one until it is a commitment we have actually tested and can keep. An unmet promise here would be worse than an honest gap.
Insurance, MSA and DPA
last reviewed ·
What we do not have
last reviewed ·
firm-level certifications · none
We do not hold SOC 2, ISO 27001, or any other third-party security certification, and we display no badge, seal or logo claiming otherwise. What we do have is publishable: real named-individual access controls, the least-privilege model shown above, and our own Secure Score trajectory, published warts and all. If your review requires a certification we do not hold, tell us directly — we would rather lose the deal honestly than pass a review we did not actually earn.
Start with a call about what you are trying to fix.
Book an assessment call30 minutes · with the engineer who would scope the work
one-page recap within 2 business days of a call that progresses